22nd Survey Division

MSRC VULN-195458 · GHSA-g5r6-gv6m-f5jv · Sydney, Australia

George Wu — ADF Veteran, independent security researcher, Sydney. I reverse malware, document techniques, and share everything for free because no one else teaches this stuff without charging hundreds.

Self-funded. Built in personal time. Given away free.
If it helps you — that's the point.

☕ Buy me a coffee 🎙️ Voice Agent — Coming Soon
☕ SUPPORTERS

"I want to go back to the fundamentals, build things myself, break things in a lab, understand them from first principles... What you've shared is worth far more than the amount I'm sending."

— @ismailjaweedahmed 10-year cybersecurity veteran

"For exposing pedo scum. Fan of your work, keep going."

— hxpnctrpstr

"For the children.. and also teach me c#nt"

— Qwenobi

"I want to go back to the fundamentals, build things myself, break things in a lab, understand them from first principles... What you've shared is worth far more than the amount I'm sending."

— @ismailjaweedahmed 10-year cybersecurity veteran

"For exposing pedo scum. Fan of your work, keep going."

— hxpnctrpstr

"For the children.. and also teach me c#nt"

— Qwenobi

RESEARCH METHOD

Adversarial thinking applied towards defensive knowledge — reverse engineering live implants captured in the wild and learning Windows OS internals.

Building techniques from first principles to actually understand them. Every case study, analysis, and home-baked demo on this site comes from non-stop failure with no support or industry experience.

I do not know everything, I learnt backwards. Because I want to give other beginners a chance to understand at a fraction of the time.

Real hacking isn't one binary that defeats every defender. It's a kill chain — a series of moves, each one building on the last. Initial access, persistence, privilege escalation, lateral movement, exfil. Most of what I document here is pieces of that chain. The defender only needs to catch one link. You need to get all of them right.

TECHNIQUES

Documented attack techniques with video proof. Each links to a full writeup.

Tired of AI that won't explain offensive techniques?

Frontier models refuse to discuss exploit development, AV evasion, or real attack chains. My voice agent tutor is different — it's trained specifically on my research and speaks in cybersecurity context without the safeguards and rate limits.

Run it locally with your own ElevenLabs API key. No rate limits, no refusals, just my voice walking you through the material.

Get ElevenLabs API Key →

Voice agent app requires API key to authenticate my voice model.

CONSOLE

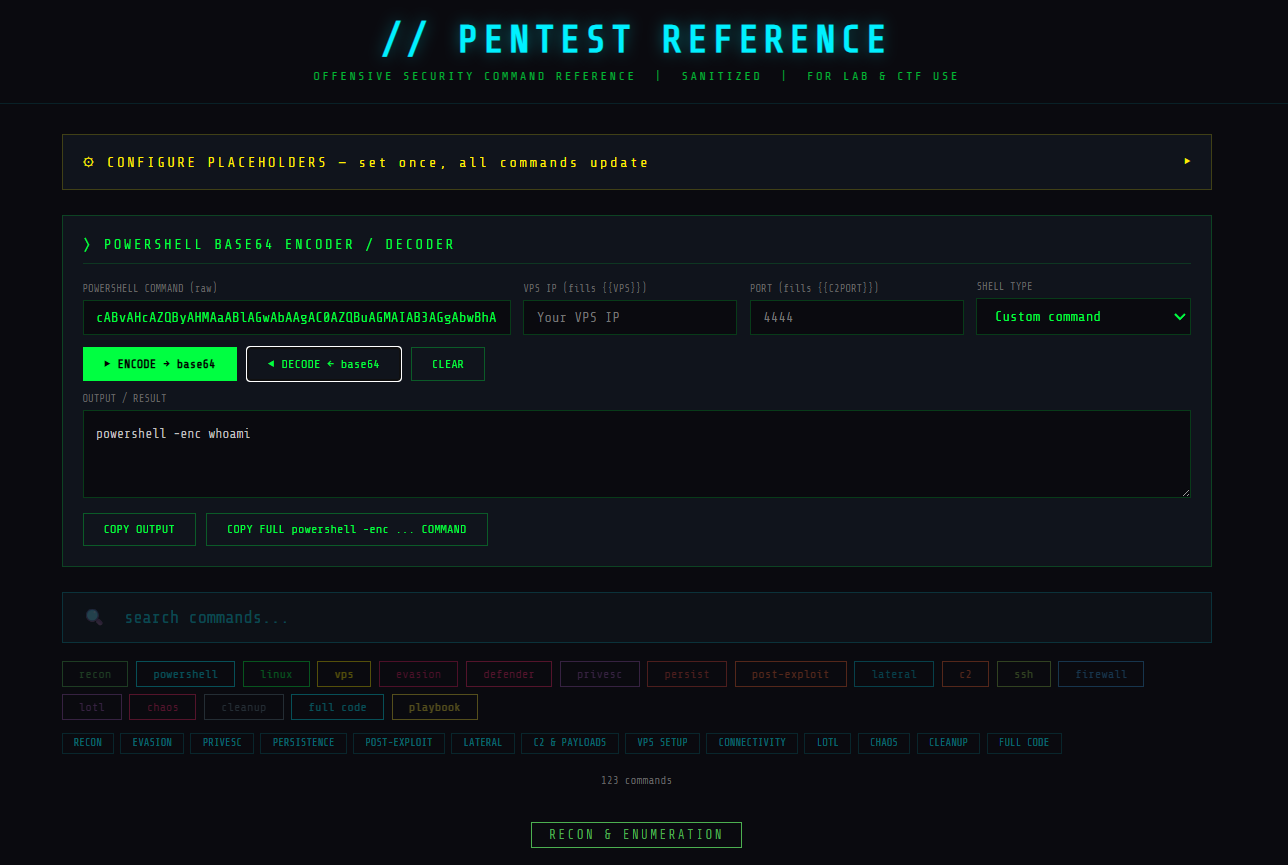
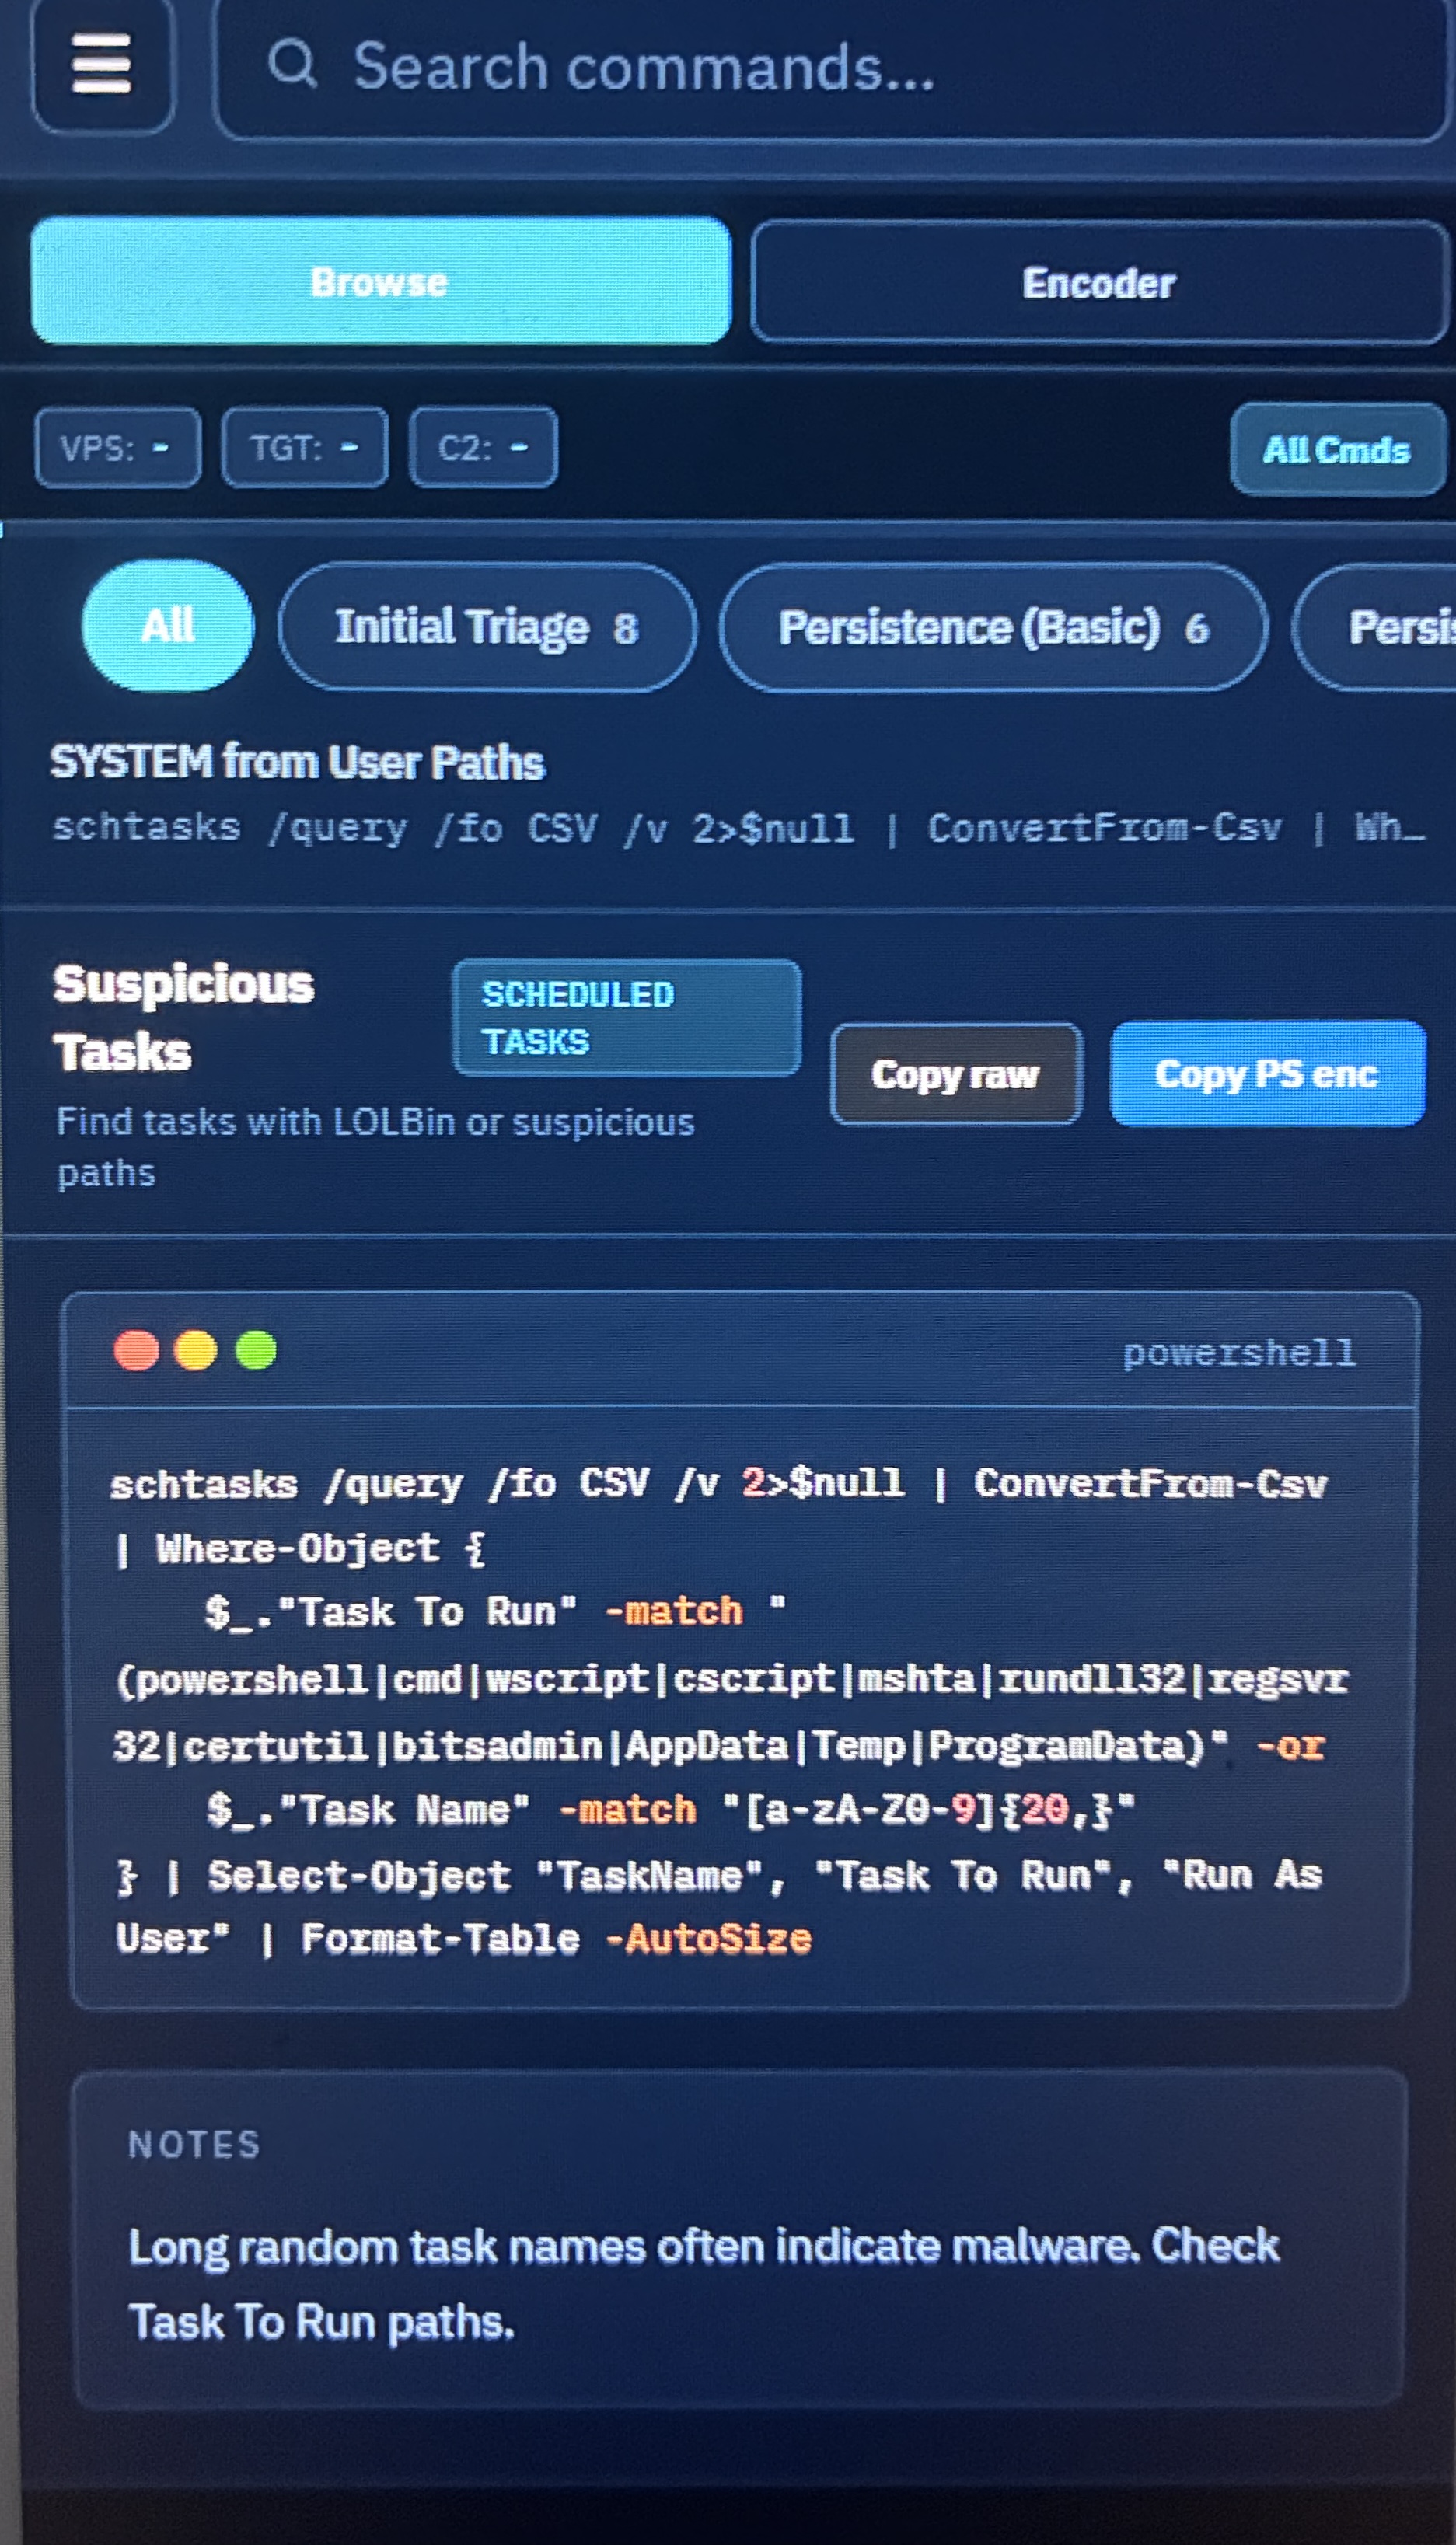
Command reference with live variable substitution

Console

🐧 LINUX / BASH
ls -laList all files with details
cd /path/to/dirChange directory
pwdPrint working directory
cat file.txtDisplay file contents
cp source destCopy file
mv old newMove/rename file
rm -rf dir/Remove directory
mkdir -p path/to/dirCreate nested dirs
whoamiCurrent user
idUser ID and groups
uname -aKernel info
hostnameMachine name
cat /etc/os-releaseOS version
df -hDisk usage
free -hMemory usage
uptimeSystem uptime
ip aIP addresses
ping -c 4 $IPPing host
netstat -tulnpListening ports
ss -tulnpSocket stats
curl -I $URLHTTP headers
wget $URL -O fileDownload file
nslookup domain.comDNS lookup
ps auxAll processes
ps aux | grep nameFind process
topLive process monitor
kill -9 PIDForce kill process
systemctl status serviceService status
systemctl restart serviceRestart service
journalctl -u service -fService logs
find / -name "*.txt" 2>/dev/nullFind files by name
grep -r "pattern" /path/Search in files
grep -i "text" file.txtCase insensitive
head -n 20 file.txtFirst 20 lines
tail -f /var/log/syslogFollow log file
wc -l file.txtCount lines
sort file.txt | uniqSort & dedupe
chmod +x script.shMake executable
chmod 755 fileSet permissions
chown user:group fileChange owner
cat /etc/passwdList users
sudo -lSudo permissions
groupsUser groups
netstat -tulnp | grep $PORTFind process on port
ss -tulnp | grep ESTABActive connections
lsof -i :$PORTWhat's using port
whois $IPIP ownership lookup
dig +short $URLDNS resolution
host $IPReverse DNS
last -a | head -20Recent logins
lastb | head -20Failed login attempts
cat /var/log/auth.log | grep -i failedAuth failures
iptables -L -n -vFirewall rules
fail2ban-client status sshdBanned IPs
arp -aARP table (local hosts)
who -aAll logged in users
wWho is doing what
tcpdump -i any port $PORT -c 50Capture traffic on port
nmap -sV -p $PORT $IPPort service scan
🪟 WINDOWS / POWERSHELL
dirList files (CMD)
Get-ChildItem -ForceList all files (PS)
cd C:\path\to\dirChange directory
type file.txtDisplay file (CMD)
Get-Content file.txtDisplay file (PS)
copy source destCopy file
move old newMove/rename
mkdir newfolderCreate directory
whoamiCurrent user
hostnameMachine name
systeminfoFull system info
Get-ComputerInfoSystem info (PS)
wmic os get caption,versionOS version
Get-WmiObject Win32_OperatingSystemOS details (PS)
net userList users
net localgroup administratorsAdmin users
ipconfig /allIP configuration
ping $IPPing host
netstat -anoNetwork connections
Get-NetTCPConnectionConnections (PS)
nslookup domain.comDNS lookup
arp -aARP table
route printRouting table
tasklistList processes (CMD)
Get-ProcessList processes (PS)
taskkill /PID 1234 /FKill process
Stop-Process -Id 1234Kill process (PS)
Get-ServiceList services
Get-Service | Where Status -eq RunningRunning services
Restart-Service servicenameRestart service
dir /s /b *.txtFind files (CMD)
Get-ChildItem -Recurse -Filter *.txtFind files (PS)
findstr /si "pattern" *.txtSearch in files
Select-String -Path *.txt -Pattern "text"Grep equivalent (PS)
Get-Content file.txt | Select -First 20First 20 lines
Get-Content file.txt -Tail 10 -WaitFollow file (PS)
reg query HKLM\SOFTWAREQuery registry
Get-ItemProperty HKLM:\SOFTWARE\*Registry (PS)
setEnvironment vars (CMD)
Get-ChildItem Env:Environment vars (PS)
echo %PATH%PATH variable (CMD)
$env:PATHPATH variable (PS)
netstat -ano | findstr :$PORTFind process on port
netstat -ano | findstr ESTABLISHEDActive connections
netstat -bConnections with process names
whoami /groups | findstr /i "admin"Check admin membership
whoami /privCurrent privileges
nslookup $IPReverse DNS lookup
Get-NetTCPConnection | Where State -eq EstablishedActive TCP (PS)
Get-NetTCPConnection -LocalPort $PORTWho's on port (PS)
Get-EventLog Security -Newest 50 | Where EventID -eq 4625Failed logins
Get-WinEvent -FilterHashtable @{LogName='Security';ID=4625} -MaxEvents 20Logon failures (PS)
netsh advfirewall show allprofilesFirewall status
netsh advfirewall firewall show rule name=allAll firewall rules
arp -aARP table (local hosts)
route printRouting table
quserLogged in users
query sessionActive sessions
Hostile Recon
Port scanners & network probes targeting this server
Loading...
24h: 0 Blocked: 0 ↓ scanner-ips.json

-

Type -
Path -
Time -
Attempts 1
Location
Country -
City -
ISP -
ASN -
User Agent
-

ABOUT

22nd Survey Division is the independent security research practice of George Wu — ADF Veteran based in Sydney, Australia. Registered as Occupation Force Callsign GSW Pty Ltd.

RESEARCH

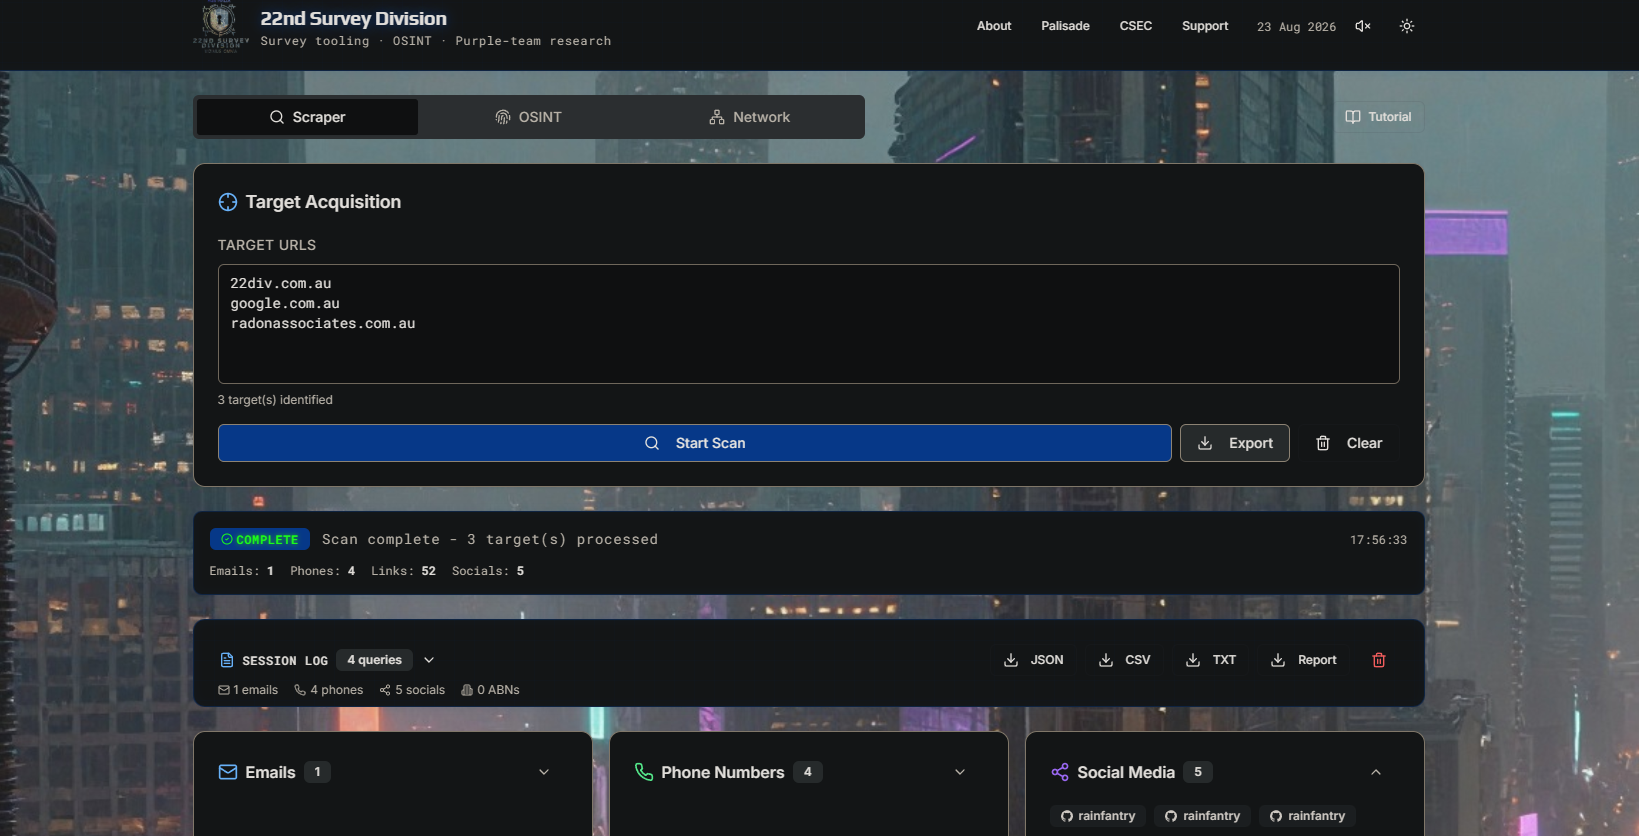
CVE submissions, MSRC disclosures, responsible PoC documentation. Everything goes public after vendors patch. Code ships, not PDFs.

PARTNERSHIPS

This site includes affiliate links to tools I actually use. When you sign up through these links, I may earn a commission at no extra cost to you. It helps keep the research free and the servers running.

Current partners: ElevenLabs

ACKNOWLEDGEMENT

This work has a mentor — an Israeli security researcher and former IDF operator whose name stays private. He showed me what real work looks like. Soldier to soldier, that was enough.

GitHub

AI VOICE AGENT

My voice model is trained on all content here. Want it to explain concepts? You'll need an ElevenLabs API key — get one here →

☕ Support the Research

SUPPORTERS

"I want to go back to the fundamentals... What you've shared is worth far more than the amount I'm sending."

— @ismailjaweedahmed 10-year veteran

"For exposing pedo scum. Fan of your work, keep going."

— hxpnctrpstr

"For the children.. and also teach me c#nt"

— Qwenobi

"I want to go back to the fundamentals... What you've shared is worth far more than the amount I'm sending."

— @ismailjaweedahmed 10-year veteran

"For exposing pedo scum. Fan of your work, keep going."

— hxpnctrpstr

Thanks for reading.

This is what I do in my spare time. I'm not trying to sell you a course or become famous. I just think security knowledge shouldn't be gatekept behind expensive certifications. If this helped you, pass it on.

Star on GitHub →

Get in Touch

×