22nd Survey Division

Tired of AI that won't explain offensive techniques?

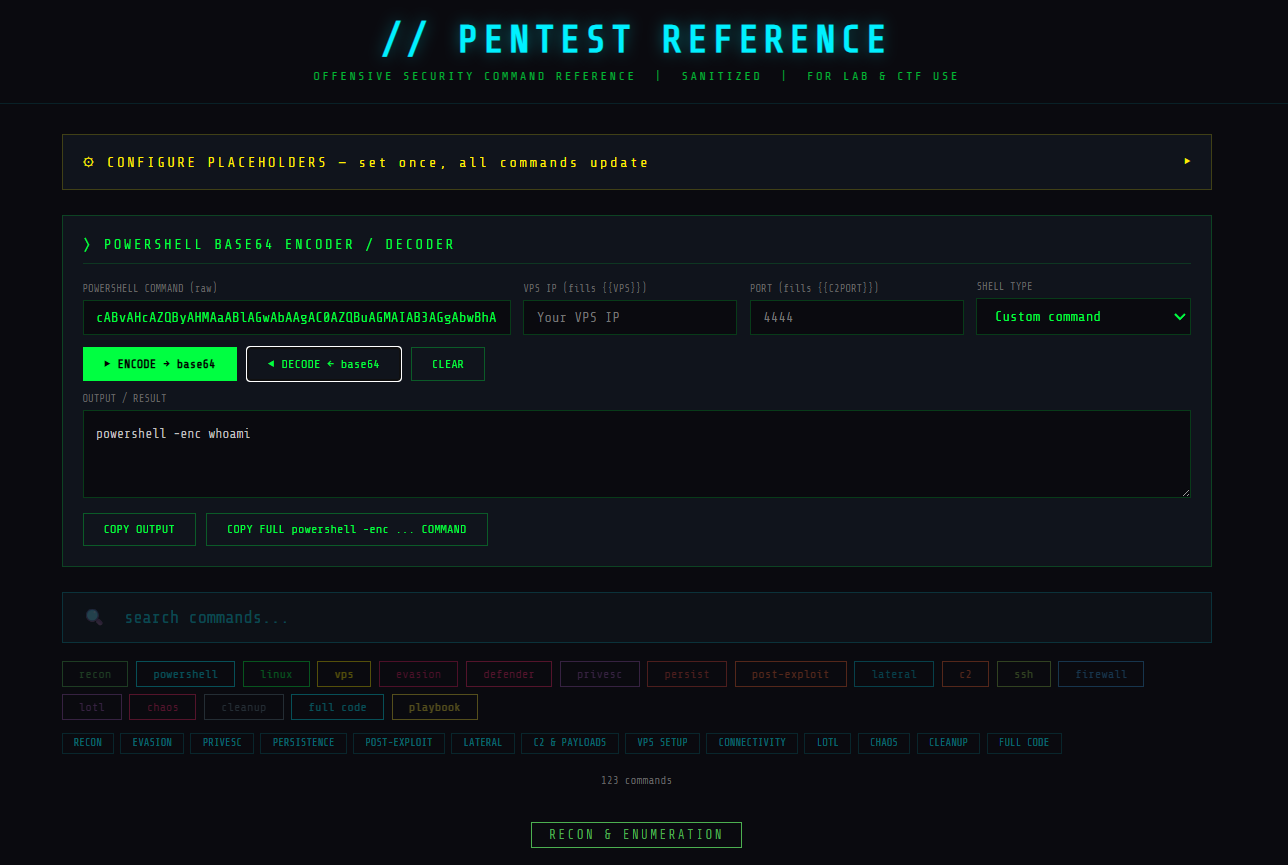
Frontier models refuse to discuss exploit development, AV evasion, or real attack chains. Cypher — my voice agent tutor — is trained on all 22div research and speaks in cybersecurity context without the safeguards.

The agent in the corner is live and free to try — but sessions are capped at 5 minutes per visit. For unlimited access, head to voice-agent.html and enter your own ElevenLabs API key. Your key, your usage, no caps.

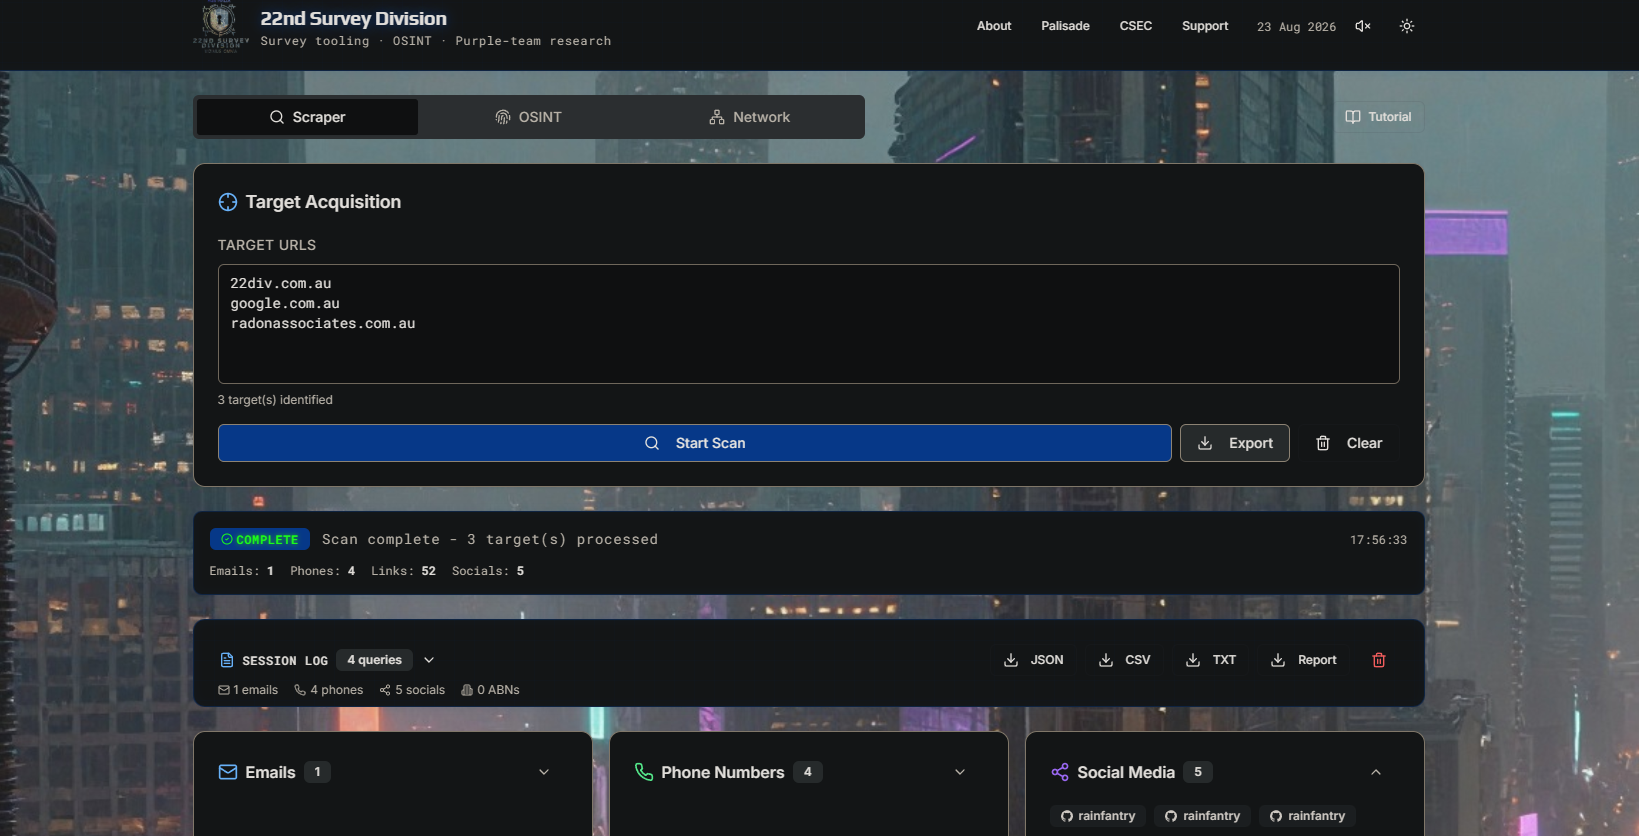
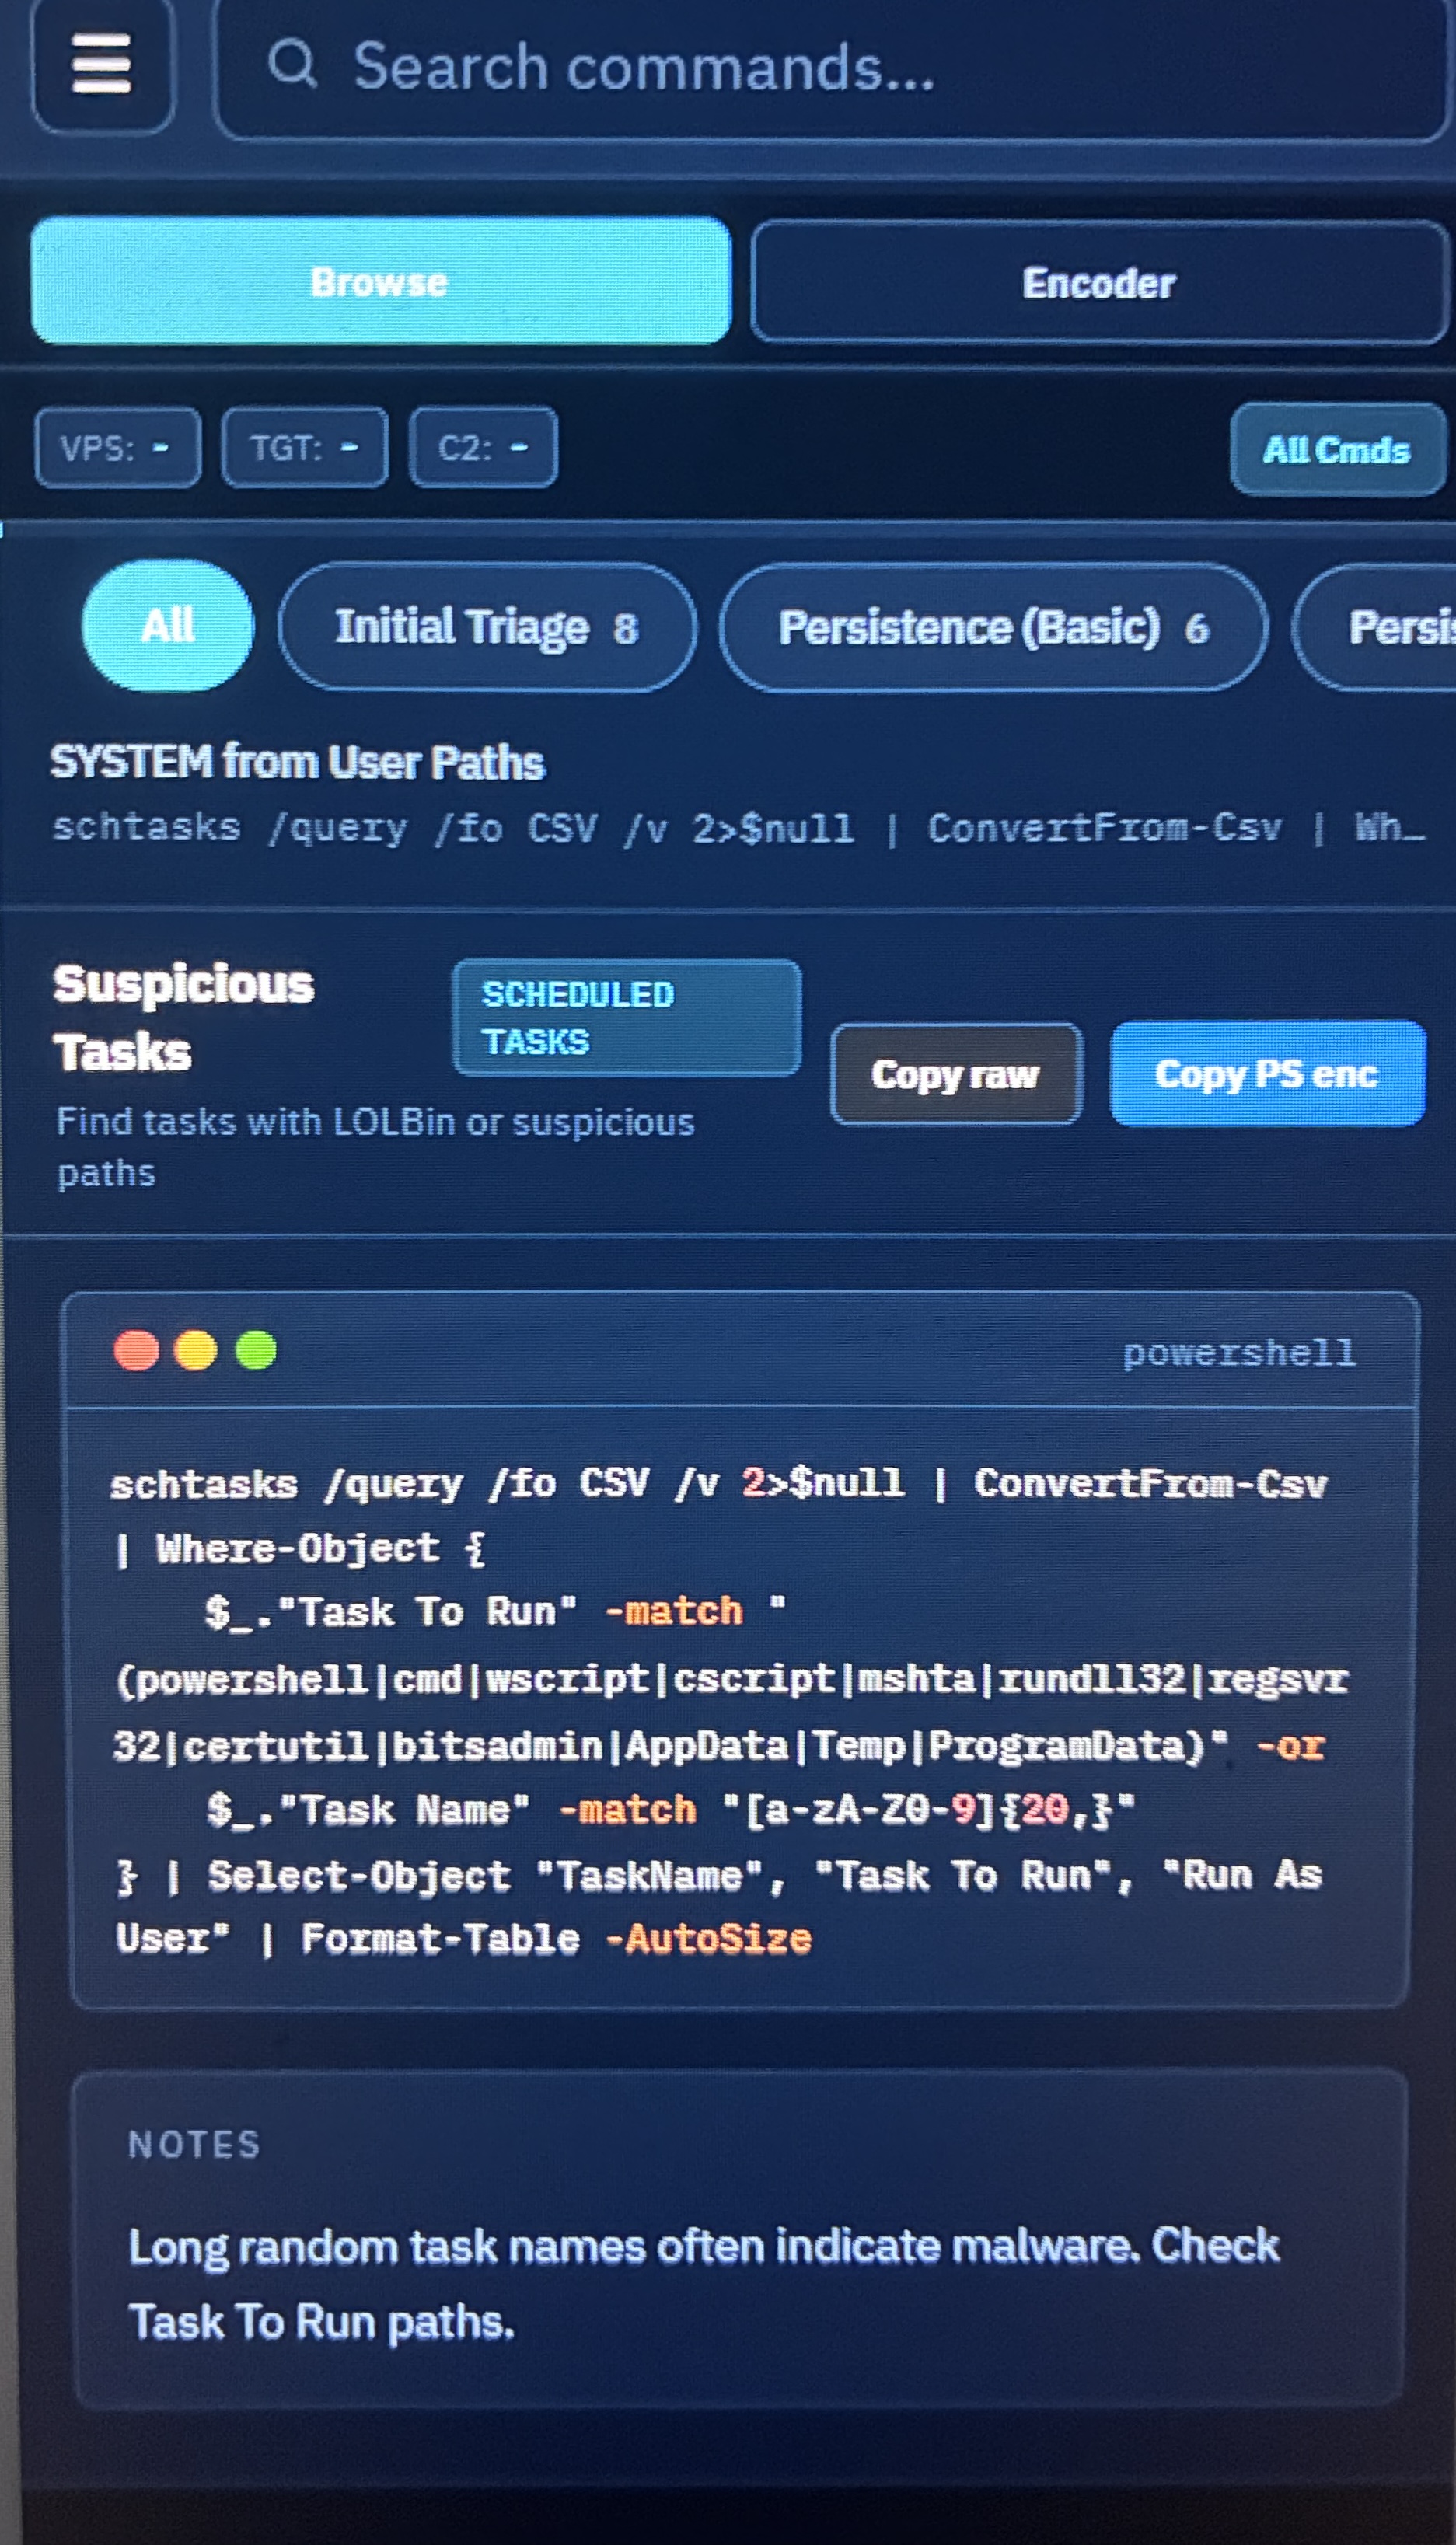
USE CASE — Blue team reference + voice agent tutor in practice

🎙️ Unlimited Access → Get ElevenLabs Key →

RED TEAM RESEARCH, DOCUMENTED OPENLY  ·  BLUE TEAM REFERENCE, FREE FOREVER

DOCUMENTED TECHNIQUES

☕ Buy me a coffee

RESEARCH METHOD

George Wu — ADF Veteran, independent security researcher, Sydney. I reverse malware, document techniques, and share everything for free because no one else teaches this stuff without charging hundreds.

Self-funded. Built in personal time. Given away free. If it helps you — that's the point.

Adversarial thinking applied towards defensive knowledge — reverse engineering live implants captured in the wild and learning Windows OS internals.

Building techniques from first principles to actually understand them. Every case study, analysis, and home-baked demo on this site comes from non-stop failure with no support or industry experience.

I do not know everything, I learnt backwards. Because I want to give other beginners a chance to understand at a fraction of the time.

CVE RESEARCH

Reported vulnerabilities — filed, credited, and documented

GITHUB

Public activity · contributions · security credits

GitHub contribution graph
47 repos 15 followers 4,326 contributions this year PRO github.com/rainfantry →
🛡
GITHUB SECURITY ADVISORY · CREDITED RESEARCHER
CVE-2026-73498 — mcp-atlassian: Arbitrary File Read via Path Traversal
GHSA-g5r6-gv6m-f5jv  ·  CVSS 7.7 High  ·  Patched 0.22.0  ·  Credit: rainfantry + Samielakkad
View Advisory →

OPEN SOURCE

Public research, tools, and proof-of-concept implementations

Loading repos…
github.com/rainfantry →

Below is a live feed of traffic hitting this website. Most of it is from bots. This website is a student portfolio. A personal playground for testing and learning. There is nothing to steal. Only you are watched.

HOSTILE RECON

Live feed of port scanners and network probes targeting this server

Hostile Recon
Port scanners & network probes targeting this server
Loading...
24h: 0 Blocked: 0 ↓ scanner-ips.json

-

Type -
Path -
Time -
Attempts 1
Location
Country -
City -
ISP -
ASN -
User Agent
-

ABOUT

This website is an open-sourced compilation of student research and practical work for ongoing studies.

GitHub
☕ Support the Research
☕ Buy me a coffee

SUPPORTERS

"I want to go back to the fundamentals... What you've shared is worth far more than the amount I'm sending."

— @ismailjaweedahmed 10-year veteran

"For exposing pedo scum. Fan of your work, keep going."

— hxpnctrpstr

"For the children.. and also teach me c#nt"

— Qwenobi

"I want to go back to the fundamentals... What you've shared is worth far more than the amount I'm sending."

— @ismailjaweedahmed 10-year veteran

"For exposing pedo scum. Fan of your work, keep going."

— hxpnctrpstr

ATTACK PRIMITIVE INTEL

Microsoft Patch Tuesday CVEs — classified by technique, not just severity

Total CVEs: —
Exploited in Wild: —
Likely Exploited: —
CISA KEV: —
Updated: —
Loading attack primitive intel...
Source: Microsoft MSRC CVRF API · Updated after each Patch Tuesday · raw JSON

Thanks for reading.

This is what I do in my spare time. I'm not trying to sell you a course or become famous. I just think security knowledge shouldn't be gatekept behind expensive certifications. If this helped you, pass it on.

Star on GitHub →

Get in Touch

×